
Security Operations

DLink dir655 rev B firmware reverse engineering – part 1
Intro Recently I stumbled upon Paul dot com blog post Reverse Engineering Firmware Primer and decided to see if I could repeat the process and to test my newly installed Debian VM packed with RE tools. Here is my take on the task. To repeat the steps one generally needs binwalk and cpio. Walk through…

Setting up capstone (Debian Wheezy)
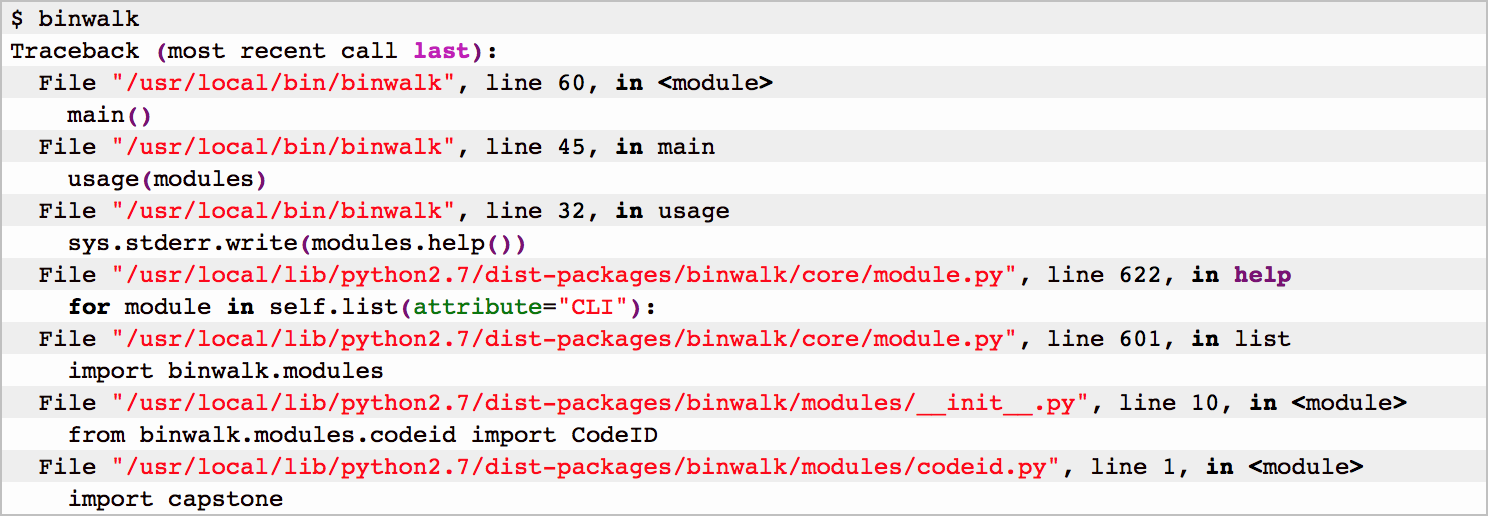
Intro Recently I’ve decided to dedicate a fresh Debian environment for my RE tools and having binwalk seemed as a good idea so I can play with firmware binaries. I followed the general install instructions from the project wiki and it seemed that all the dependencies were installed. On starting the executable however I got…

Practical Reverse Engineering Exercises – Ch1-Ex2 – Write-Up
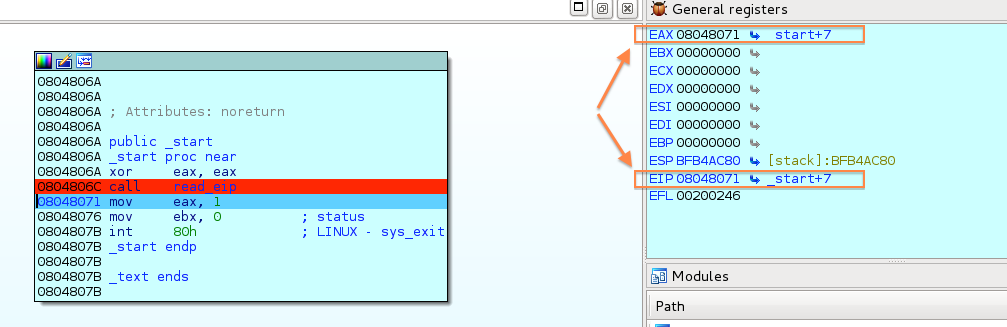
Intro This is the second post of a blog series following my progress with the “Practical Reverse Engineering: x86, x64, ARM, Windows Kernel, Reversing Tools, and Obfuscation”, Bruce Dang, Alexandre Gazet, Elias Bachaalany, Sebastien Josse, ISBN: 978-1-118-78731-1. The book includes number of exercises and the authors encourage the people to blog their solutions. The solutions…

Practical Reverse Engineering Exercises – Ch1-Ex1 – Write-Up
Intro This is the first post of what should be a blog series following my progress with the “Practical Reverse Engineering: x86, x64, ARM, Windows Kernel, Reversing Tools, and Obfuscation”, Bruce Dang, Alexandre Gazet, Elias Bachaalany, Sebastien Josse, ISBN: 978-1-118-78731-1. The book includes number of exercises and the authors encourage the people to blog their…

Fix the problem, not just point at it – thoughts on the “bug hunting” initiatives etc.
I have been thinking a lot about the fact that the panetesting, sourco code reviews and all those security assurance problems just point out the problem. Fixing the discovered application security issue however is a prerogative of the developers which unfortunately are still lacking security expertise. Bug hunters and zero days discoverers have been long…

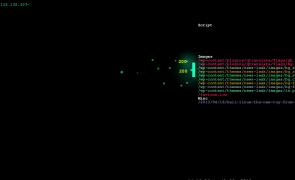
Visualise your Apache logs with logstalgia
Couple of days ago a colleague of mine (thanks DL) got my attention with a lovely web server access log visualization tool called “logstalgia” (opensource c++ project). Well you can read the description by yourself on the project site but with few words – it gives you the amusing option to “play” your Apache or…
Saving data from “dying” HDD – LVM & ext3
Couple of days I restarted my machine running Debian Wheezy and for my surprise I was not able to boot. I was using encryption for the entire disk. I was able to unlock the disk but not able to mount the partitions. Nice … time to panic … After I took enough time panicking I…

Malware Sandbox – Free Public Cuckoo instance
I’m writing this down for my own reference and if someone else benefits this I’ll be more than happy. Here is the URL (https://malwr.com/) to the public cuckoo sandbox – free to submit executables for malware analysis. Enjoy
HTTP Basic Authentication Dictionary and Brute-force attacks with Burp Suite
HTTP Basic Authentication brief explanation HTTP supports several authentication mechanisms. Upon a request for resource within a protected space the server should respond with authentication challenge using WWW-Authenticate header. In order to receive authorization the client should send requested identification information using Authorization header. When the client is not authorised a 401 “Unauthorised” response status…
forum.arenabg.com members table dumped and published in the Internet
Yesterday a partial dump containing email addresses and hashed passwords for the forum.arenabg.com members leaked. According to The Hackers News the leak was published by a Russian hacker. I will not comment the story, but if you ever used forum.arenabg.com make sure that you not reuse the same password for your email or somewhere else.…


Recent Posts
Tags
bruteforce bug bounty bug hunting Burp Suite d3 data leak data recovery dictionary entropy pool fix fuzzing hackaday image processing Journalistic tools log analysis malware mindmap online courses Practical Reverse Engineering randomness sandbox skype SQL injection SSL technical visualisaiton visualisation Vulnerability Management Wanda the fish Zeus