
Year: 2013

How to emulate Gaussian blur in iDraw
I am sorry but this is not a security related blog post. However I still consider some workarounds as “life hacks” and if someone could benefit the shared info I will be most than happy. I recently started using iDraw and while working on some of my old drawings made with InkSkape I have noticed…

Cool visualisation ideas
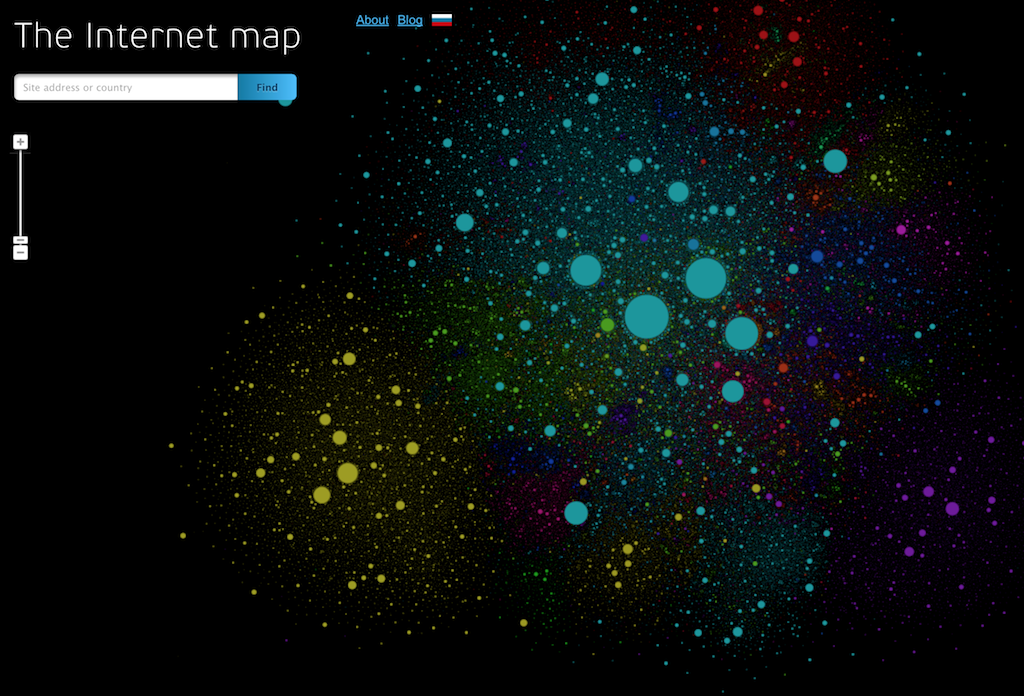
I have always admired people that could represent complex ideas in a simple way or have come up with ideas to visualise complex/big data in a graspable manner. Here is my personal collection of cool visualisations. If you have anything cool in your own collection, please drop me a line Enjoy! Internet map

Vulnerable web applications to play with
This is just a list with applicaitons and frameworks out there that could be used to test your web application pentesting kung fu skills or to test your automated tools. I am trying to keep copy of those with me, because projects tend to die. So if you find that some of the links is…

Doxygen & PHP static code analysis call graphs
This post is more to document my own “discovery” and not to get into the loop of researching the same topic again and again. And if someone finds it helpful its great. I was searching for PHP static code analysis tools that generate call graphs and for my surprise the tool that I found most useful…
Fix the problem, not just point at it – thoughts on the “bug hunting” initiatives etc.
I have been thinking a lot about the fact that the panetesting, sourco code reviews and all those security assurance problems just point out the problem. Fixing the discovered application security issue however is a prerogative of the developers which unfortunately are still lacking security expertise. Bug hunters and zero days discoverers have been long…

Visualise your Apache logs with logstalgia
Couple of days ago a colleague of mine (thanks DL) got my attention with a lovely web server access log visualization tool called “logstalgia” (opensource c++ project). Well you can read the description by yourself on the project site but with few words – it gives you the amusing option to “play” your Apache or…
Saving data from “dying” HDD – LVM & ext3
Couple of days I restarted my machine running Debian Wheezy and for my surprise I was not able to boot. I was using encryption for the entire disk. I was able to unlock the disk but not able to mount the partitions. Nice … time to panic … After I took enough time panicking I…
Automatic code analysis by Deutsche Telecom
The Developer Garden (Deutsche Telecom “ecosystem”) announced a new service – automatic code analysis for applications developed using the following technologies – .NET, ASP, VB, JAVA, C/C++, PHP, RUBY, Perl, Java Script. Aside from the typical marketing sentences about what you are getting out of their product it reads “Amplify your know-how by analyzing your…
Fix metasploit “Database not connected or cache not built”
This is a short post explaining how to deal with metasploit instance not connected to its database (I’m using the new Kali Linux but it is the same for Backtrack 5). The issue usually surfaces when you try to search auxiliary or exploit. Assuming that you use msfconsole you get something like this: msf >…

Malware Sandbox – Free Public Cuckoo instance
I’m writing this down for my own reference and if someone else benefits this I’ll be more than happy. Here is the URL (https://malwr.com/) to the public cuckoo sandbox – free to submit executables for malware analysis. Enjoy




Recent Posts
Tags
bruteforce bug bounty bug hunting Burp Suite d3 data leak data recovery dictionary entropy pool fix fuzzing hackaday image processing Journalistic tools log analysis malware mindmap online courses Practical Reverse Engineering randomness sandbox skype SQL injection SSL technical visualisaiton visualisation Vulnerability Management Wanda the fish Zeus