
Year: 2012

GDBOP website malfunctioning … again
I just found out, with no surprise, that the website of GDBOP (Bulgarian government cybersecurity team) hosted on http://www.cybercrime.bg does not function properly … again. The reason is that the the front-end app cannot connect the back-end MySQL server. Of course the error is not handled securely :). I wonder how long it will take…

Security source code review scoping questionnaire
Usually when a customer comes with request for security source code review one of the main questions is “How long it will take?”. And the answer of that particular question is not an easy one because it depends on so many factors: – application architecture and complexity – documentation absence or presence – code quality…

Teach your students to cheat
In one of his latest posts Bruce Schneier refers to an interesting article authored by two Marylend University professors. They carried out interesting examination for their information security course. The idea was to provoke their students creative and out of the box thinking to break the american education system stereotypes. In order to pass the…
An Introduction To Keyloggers, RATS And Malware – book review
Yesterday I stumbled across yet another “hacking” site. My curiosity motivated me to mirror the site content and go through all the files. Most of them were books and tutorials. After I finished reviewing some of them I realised that I hadn’t include any book reviews in this blog so far and that may be…

Udacity – nice online computer science courses
A post outside the security field … A friend of mine sent me a link to the http://www.udacity.com/ (Thanks, Momcho!) and after I took a look and spent some time with the platform decided that it is a good idea to blog about it. Udacity is yet another site with online computer science courses and yet different…
Kaspersky Lab source code analysis of Duqu
Kaspersky Lab has been analysing the infamous duqu worm code for several months. In one of the latest writeups, Igor Soumenkov describes part of Duqu code – for which there is an open debate around what language was used for its development. The discussion is quite interesting so I compiled a list of the relevant…
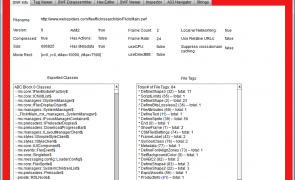
SWFInvestigator – a new tool for testing SWF files
Three days ago Adobe Labs surprised me with a beta version of their opensource Air application for SWF analysis called SWFInvestigator. It is available for download from the Adobe Labs website and the source code form the corresponding sourceforgeproject page. SWFInvestigator is a collection of small tools under common GUI umbrella. The utility is useful…
Colossus gallery fundraising initiative
British national museum of computing started conversation work of the Colossus hall. Colossus is one of the first programmable computers designed to solve cryptographic problems in 1943 by Tommy Flowers. Colossus second version was used by UK intelligence at the end of WWII to decrypt german messages encoded with Lorenz SZ40/42. Colossus use vacuum tubes…

Zero day exploits officially on sail
The 0-day exploits market was there for some time, but it was always a underground black hats territory. I’m sure that the government agencies have been buying offensive security tools but I have never seen open advertisement from a big company selling those type of things. Apparently the time is changing. VUPEN (if the name…
Hacking Lab – how and why
In one of the recent Ethical Hacking Network articles, Thomas Whilhelm, the founder of hackingdojo.com, discusses questions regarding setting up a hacking lab. The article is not a guide, but rather explanation why such thing is needed. It’s quite motivational 🙂 Enjoy!



Recent Posts
Tags
bruteforce bug bounty bug hunting Burp Suite d3 data leak data recovery dictionary entropy pool fix fuzzing hackaday image processing Journalistic tools log analysis malware mindmap online courses Practical Reverse Engineering randomness sandbox skype SQL injection SSL technical visualisaiton visualisation Vulnerability Management Wanda the fish Zeus