
Security tools

Web application security assessment scoping questionnaire
I’ve got frustrated couple of days ago when I needed to send quickly a scoping questionnaire focusing on web application security assessment and was not able to find a single one in my archives. I was sure that I’ve put together at least couple of those during the past 3 years but no find regardless…
BurpSuitePro Proxy History Logs to plain text
Couple of months ago I finally switched to BurpSuitePro after so many years using the free version and … I do not regret at all. I adapted pretty quickly to the extra options it provides compared to the free version. There are many differences between the free and the commercial product versions but this post…

Well structured SQL injection reference
There are many SQL injection cheat sheets out there, but I just stumbled upon another one. It features very nice interface to quickly find what you need. It is a work of Roberto Salgado from Websec.ca. The company also published some SQL injection challenges so you can test your skill and have fun. Enjoy!

Security source code review scoping questionnaire
Usually when a customer comes with request for security source code review one of the main questions is “How long it will take?”. And the answer of that particular question is not an easy one because it depends on so many factors: – application architecture and complexity – documentation absence or presence – code quality…

SWFInvestigator – a new tool for testing SWF files
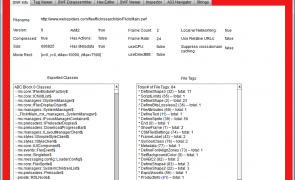
Three days ago Adobe Labs surprised me with a beta version of their opensource Air application for SWF analysis called SWFInvestigator. It is available for download from the Adobe Labs website and the source code form the corresponding sourceforgeproject page. SWFInvestigator is a collection of small tools under common GUI umbrella. The utility is useful…
Hacking Lab – how and why
In one of the recent Ethical Hacking Network articles, Thomas Whilhelm, the founder of hackingdojo.com, discusses questions regarding setting up a hacking lab. The article is not a guide, but rather explanation why such thing is needed. It’s quite motivational 🙂 Enjoy!

Anubis sandbox or “Analyse this!”
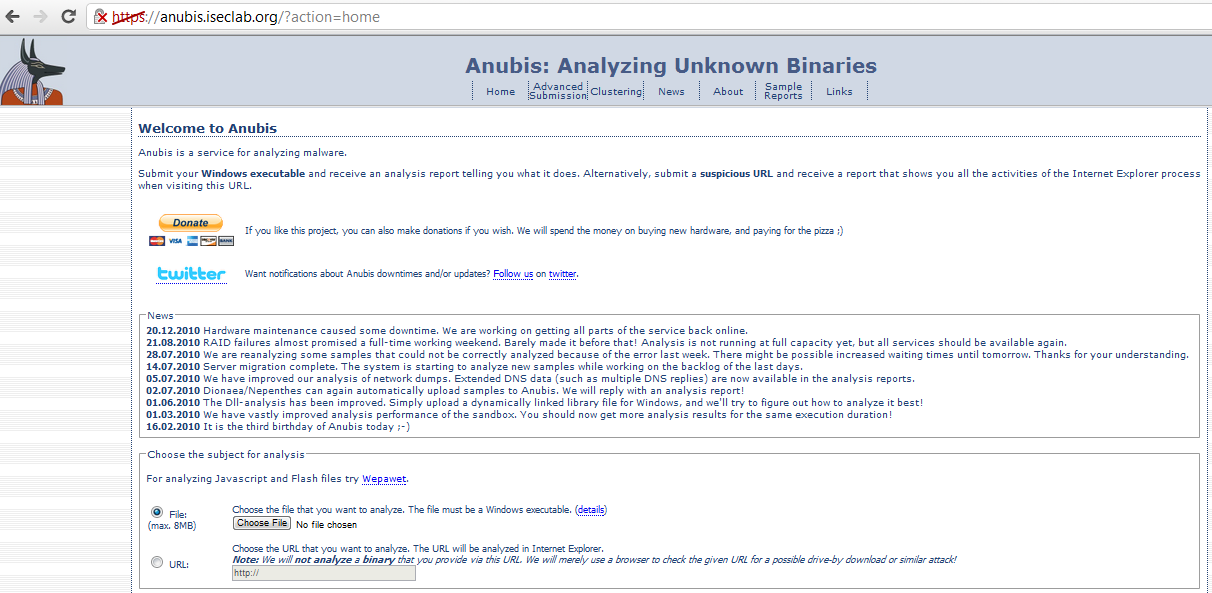
If you would like to know more about the behavior of a particular malware, but you do not want to build your own sandbox or you just have not the resources to build it then may be you can find Anubis service suitable for your needs and pretty convenient. Anubis had been developed by IsecLab.…
Qualys – free SSL test
After publishing a methodology for SSL configuration assessment, Qualys startedfree service their methodology. The result of the assessment is a grade based on 4 indicators: Certificate information Supported protocols Key exchange Cipher strength Enjoy!
Arabic names dictionary
My small contribution to the community – a dictionary with Arabic names – both male and female Arabic names dictionary @ packet storm Enjoy
BackTrack v5 – more juicy with GNOME – part1
So here it is – the new version of our beloved pentesting Linux distribution – BackTrack – is out. Thanks to all the developers that took time to put together v5. The thing that i found really exciting is GNOME interface. KDE was really annoying to me and never get used to it. Just installing…



Recent Posts
Tags
bruteforce bug bounty bug hunting Burp Suite d3 data leak data recovery dictionary entropy pool fix fuzzing hackaday image processing Journalistic tools log analysis malware mindmap online courses Practical Reverse Engineering randomness sandbox skype SQL injection SSL technical visualisaiton visualisation Vulnerability Management Wanda the fish Zeus